About us
We started Prayog Security because security should hold up in practice.
Most companies can pass an audit and still be exposed. Prayog Security builds products for that gap: Prayog One, a compliance platform built to test what your systems actually do, and Prayog Surface, launching soon. Alongside them, we run hands-on security engagements, from penetration testing to compliance readiness.
The name
The word prayog means putting something into practice.
In Hindi and Sanskrit, prayog is the act of using a thing for real: an application, a practice, an experiment that is actually carried out. It is the opposite of a plan that stays on paper.
That is the whole idea behind the company. A control only counts if it works when someone tests it.
Why we started
Passing the audit and being secure should be the same work.
Most security teams are not careless. They are stretched. They write the policy, gather the screenshots, sit through the audit and pass, and still wonder whether the person who left really lost access, or whether that storage bucket is still open.
Our founder has spent his career in that gap, from both sides of the table: building controls and checking them. Prayog Security exists so the work you do for the auditor is the same work that keeps attackers out, and so it is done once.
What we hold ourselves to
In practice, not on paper
We test what systems do, not what documents say they do.
People decide
Our tools propose changes. A person approves every one.
Straight answers
We say what Prayog One is built to do, and we will tell you when we are not the right fit.
Built in India
We work from Goa, for teams here first, with data and compute in India.
Who is behind it
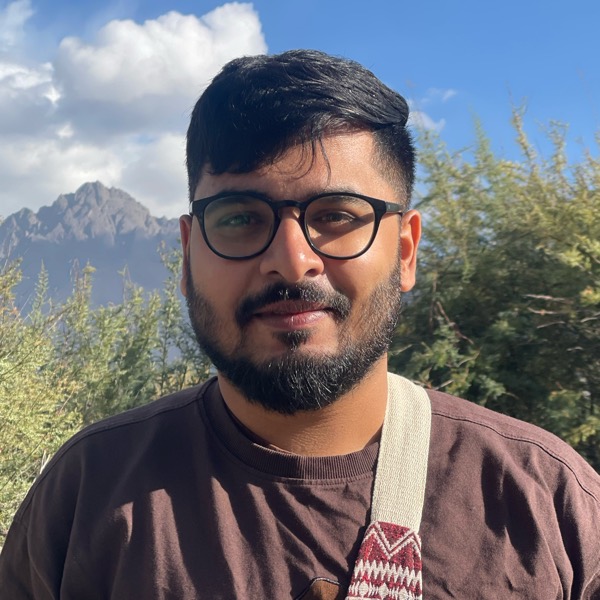
Vipul Soman
Founder, Prayog Security
A security architect based in Goa. His work spans security operations, security consulting and enterprise security architecture.
How we handle your data
We treat your data the way we would advise you to.
Security work means seeing things you would not show anyone else. This is how we look after them.
Agreement first
We sign a non-disclosure agreement and agree the scope in writing before we touch any system.
Only the access we need
We ask for the least access the work needs, read-only wherever it will do, and remind you to remove it when we finish.
Kept encrypted
Findings, reports and anything we collect stay encrypted on our own managed devices, shared only with the people you name.
Deleted when done
Within 30 days of the engagement ending we delete working data and confirm it in writing. We keep the final report for our records.
Found a security issue in our own site? Here is how to report it